Securing Online Retail and D2C Brands Across India
E-commerce in Tamil Nadu and across India is undergoing unprecedented growth. However, along with higher transaction volumes comes increased scrutiny from cybercriminals targeting payment checkouts, personal customer records, and admin dashboards. A single security breach can destroy customer trust and incur severe financial penalties under India's Digital Personal Data Protection (DPDP) Act 2023.
1. SSL/TLS Encryption & PCI-DSS Compliant Payment Gateways
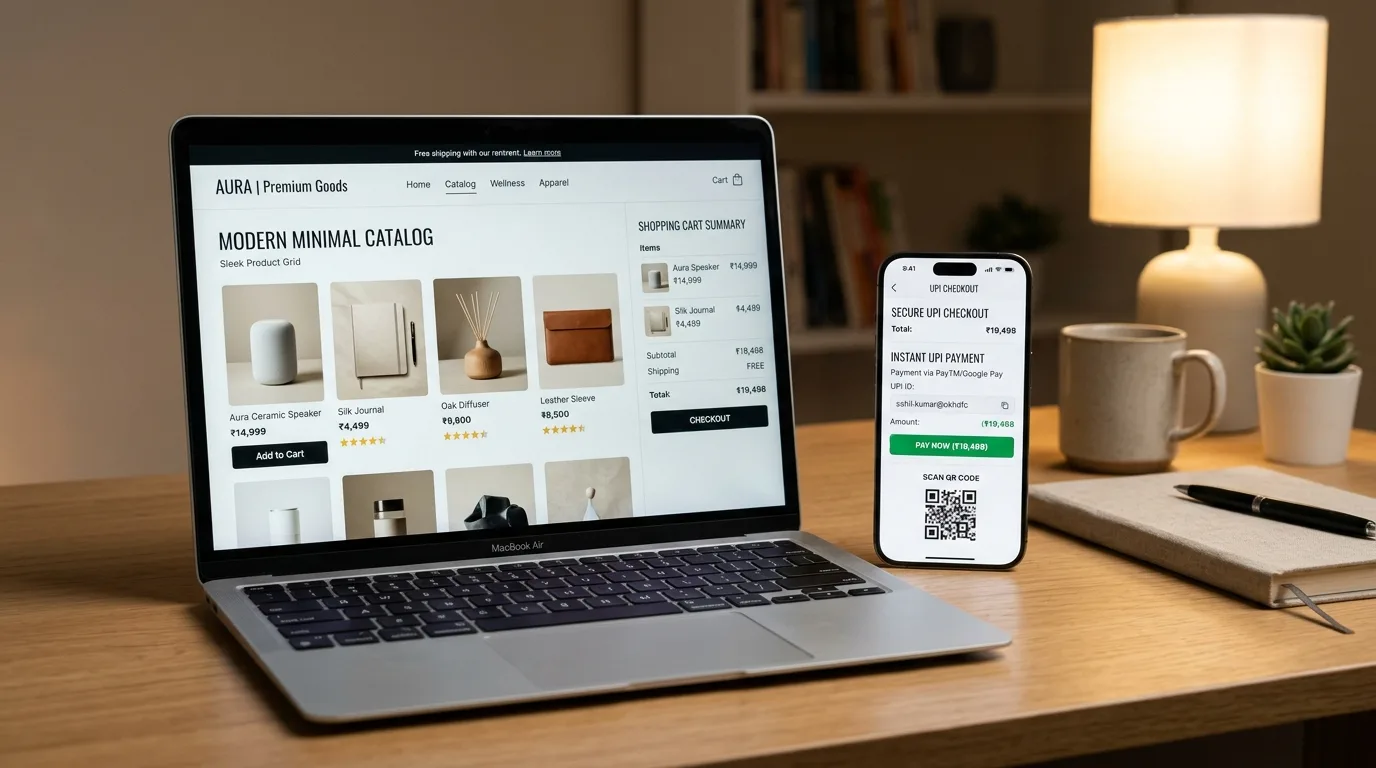
Every commercial web store must enforce modern TLS 1.3 encryption across all URLs. Furthermore, store owners should never handle raw credit or debit card numbers on their own servers. By integrating PCI-DSS Level 1 compliant gateways (such as Razorpay, PayU, or Cashfree) using hosted checkout modals or tokenization, cardholder data is securely transmitted directly to certified banking servers without ever touching your local database.
2. Defending Against SQL Injection & Cross-Site Scripting (XSS)
SQL injection and XSS remain the most common attack vectors against insecure e-commerce websites. Attackers inject malicious query parameters into product search fields or checkout inputs to extract user databases or hijack customer session cookies. Utilizing parameterized SQL queries, modern ORMs, and strict Content Security Policies (CSP) effectively neutralizes these vulnerabilities.
3. Multi-Factor Authentication & Admin Access Lockdown
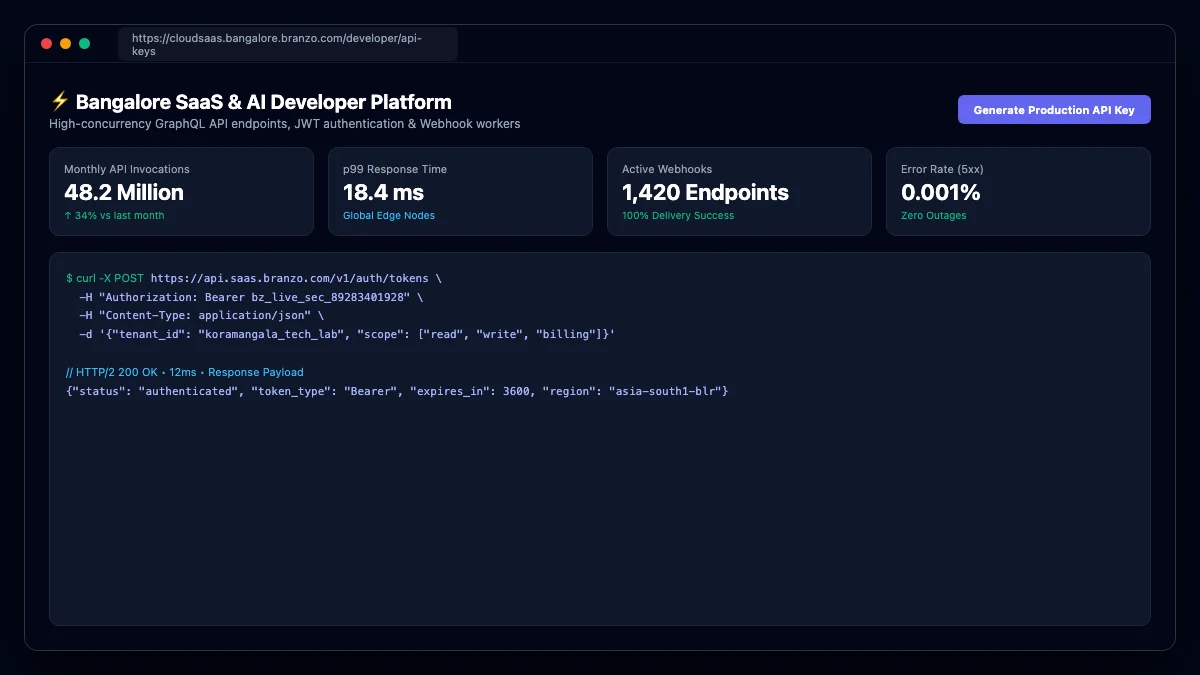
Brute-force attacks against administrative login portals account for the majority of store takeovers:
- ✓ Enforce MFA/2FA: Require hardware tokens or authenticator apps (OTP) for all administrative staff accounts.
- ✓ Rate Limiting: Block IP addresses that fail more than 5 consecutive login attempts.
- ✓ Role-Based Permissions (RBAC): Grant catalog managers and support staff only the minimum necessary privileges.
- ✓ Automated Daily Off-Site Backups: Store encrypted daily database snapshots on isolated cloud storage buckets (AWS S3) to ensure rapid disaster recovery.
4. Conclusion & Ongoing Security Audits
Cybersecurity is not a one-time checkbox—it is an ongoing operational commitment. Regular vulnerability patching, code reviews, and firewall monitoring protect your business reputation and customer trust. Contact Branzo Techno Solution in Coimbatore for e-commerce development and security audits.
Founder and technical director at Branzo Techno Solution, Coimbatore. Directing custom web design, mobile app architecture, and enterprise software engineering across Tamil Nadu.